In-region endpoint selected for the company.
Features · Enterprise
Data your security team can sign off.
Review where company data lives, how access is challenged, and the line HR cannot cross into individual health.
Review surfaceFacts in scope
Tenant boundaryCompany-scoped
Residency4 instances
Health visibilityAggregate only
Lab agreementPipeline only
Data location
Four regional instances. One onboarding decision.
Each company is an isolated tenant. Company ID is carried throughout the platform, and lab or health-risk queries remain company-scoped.
In-region endpoint selected for the company.
In-region endpoint selected for the company.
In-region endpoint selected for the company.
No later switchThe company chooses its instance at onboarding. Changing that choice later requires a migration.
Authentication controls
Exact controls, not broad assurances.
Access behavior differs by flow and platform. These are the values an implementation or security reviewer can check.
ControlValueScope
Password lockout5 failed attemptsAccount locks
Reset link1 hourSingle-use
Password length8 reset / 6 changeTwo separate flows
OTP10 minutesCountry-configurable
Mobile pinningTrustKitiOS and Android
CaptchaEnabledNon-mobile web and admin
Employee health boundary
HR sees the crowd, not the person.
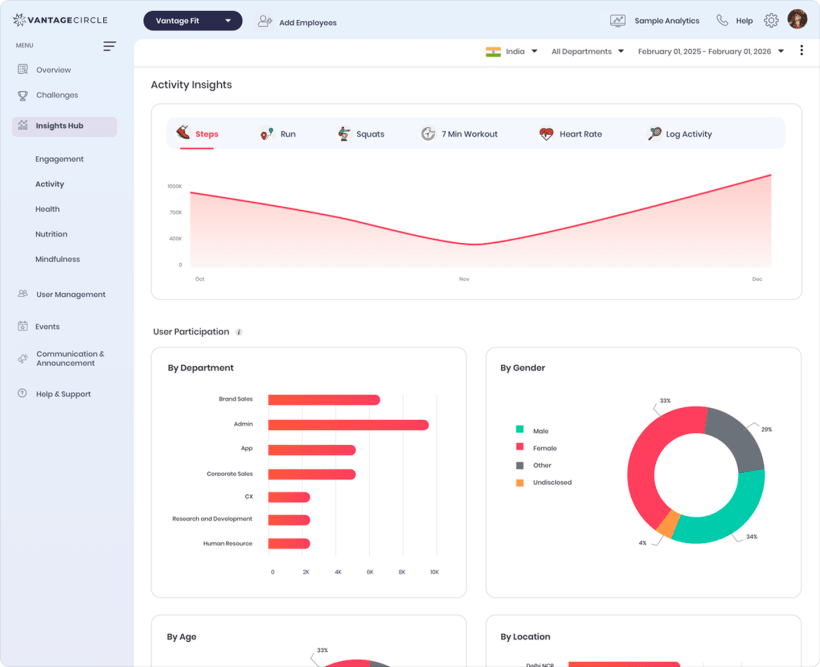
Participation reporting can move upstairs because private health inputs do not. The dashboard separates program activity from an employee’s health record.
Program and aggregate views
Organization and department participation metrics, enrollment, active rates, challenge participation, and leaderboards remain available for program operations.
OrganizationAggregate metrics
DepartmentProgram metrics
ChallengeParticipation
An individual health record
Private employee inputs stay outside the admin view.
Health profile, weight, or BMIHRA answers or individual risk categoryLab report or biomarker valuesMood, food diary, or sleep log
Health-risk audiences return a count, never a name list.
“The list of users is not displayed to protect individual privacy.”
Aggregated buckets in. No PII out.
The read-only AI view uses aggregate signal buckets through an internal ML API. It does not receive personally identifiable information. Health Insights is a separate whitelist-only module.
Hash identity. Clear tokens.
Name and email are hashed, sessions are cleared, and historical activity or transaction records remain for reporting. Availability is company-configurable.
HIPAA-guideline aligned.
BAA provisions for HIPAA compliance apply to the lab-report pipeline only. This scope does not extend to the platform as a whole.
Continue the enterprise review
Follow the boundary into the enabled modules.
Bring the review team
Walk through the controls in your operating context.
Review tenant scope, residency, authentication, employee visibility, deletion behavior, and the lab-pipeline agreement. Region is standard at onboarding, SAML setup is integration-led across tiers, and Wellness Leagues are annual.
Company isolationFour regionsAggregate health viewsScoped lab provisions