Regional instance
Features · Enterprise
Data your security team can sign off.
Employee wellness platform data privacy starts with four regional instances and isolation scoped to the company. HR sees a crowd, never a name list. That is how the participation number stays usable upstairs.
India, US, EU, UAE Aggregate only 100+ organizations
Four regions. No later move.
You choose India, US, EU, or UAE at onboarding. Employee data stays in that regional instance. In-region endpoints handle requests. Changing region later is a migration, not a setting.
Regional instance
Regional instance
Regional instance
EU residency is available. Residency is not a compliance badge. This is not a dedicated data center in your city.
The numbers a reviewer will ask for.
Corporate wellness platform security at the auth layer is specific. SAML 2.0 is set up by the integration team. The rest is on every password and OTP path.
Failed password attempts lock the account. Unlock starts a reset.
Single-use. New password on reset must be at least 8 characters.
A different flow. In-app change password minimum is 6 characters.
Valid for 10 minutes. Configurable per country.
SSL pinning on iOS and Android.
On non-mobile web and the admin console.
IdP names and roster systems live on Integrations. This page stops at the auth facts.
Count only. Never a name list.
Admins see company and department aggregates. They cannot open an individual health profile, HRA, lab values, or mood. Health-risk targeting returns a count.
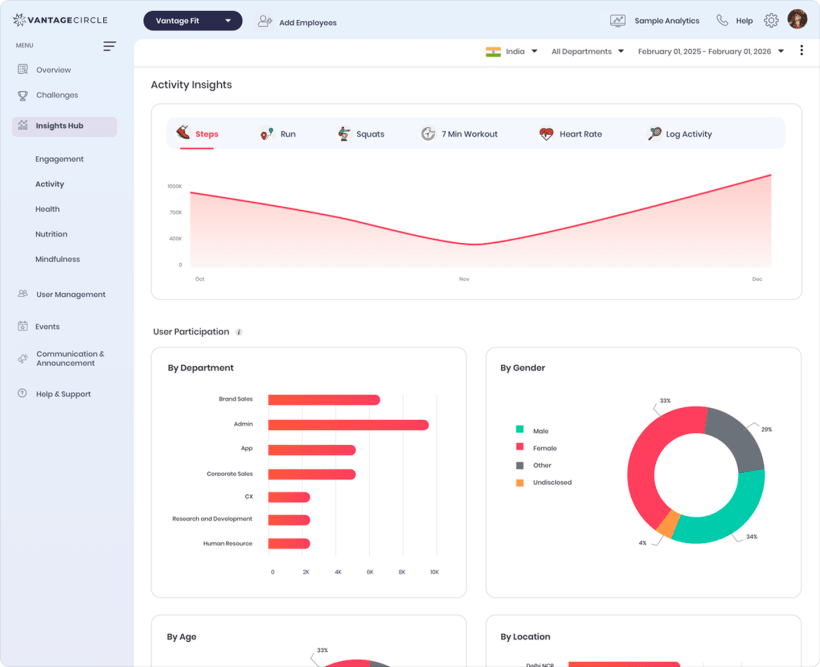
Enrollment, active users, participation rate
Challenge standings and last-active dates
Org-level prevalence if Health Data Upload is on
Weight, BMI, HRA answers, mood, or labs
A named health-risk roster
The list of users is not displayed to protect individual privacy.
Dashboard figures are a product view, not a client result. HIPAA-guideline aligned on this point.
Insights without names. A BAA on the lab pipe.
Leadership Insights are AI observations from aggregated buckets. No PII. Read-only. They do not change your config.
Leadership Insights
Internal ML API. Aggregated signal buckets only. Not predictive. Not a person-level feed.
Account deletion
Name and email are hashed. Tokens are cleared. Historical activity and transaction records stay for reporting.
BAA provisions
BAA provisions for HIPAA compliance apply to the lab-report pipeline. Not a HIPAA-compliant platform claim.
Health Data Upload owns the extraction flow. This page owns the boundary.
Before you send it to legal
Can HR open an individual’s labs or HRA?
No. Admins see company and department aggregates. Health-risk targeting returns a count only. The list of users is not displayed to protect individual privacy.
Is Vantage Fit a HIPAA-compliant platform?
No. There are BAA provisions for HIPAA compliance on the lab-report pipeline. The platform is HIPAA-guideline aligned on what HR can see. That is not a blanket HIPAA-compliant platform claim.
Can we change region after go-live?
Not without a migration. Region is India, US, EU, or UAE, chosen at onboarding.
Review the facts. Then book the room.
Walk through residency, lockout rules, and the aggregate-only health view with your security reviewer in the call.
Four regions
Company-scoped
Count only
BAA on labs
Trusted by 100+ organizations. Packet contents are shared in the review, not invented here.