Data your security team can sign off.
Written for a due-diligence review rather than a badge row. Every line is a product fact, and the claims this page does not make are listed before the questions.
- Data residency
- India, US, EU or UAE. Chosen at onboarding.
- Tenancy
- Company-scoped. Every query carries the company.
- Sign-in
- SAML 2.0 SSO, password, email OTP.
- Admin visibility
- Aggregates. No individual health record.
- AI
- Leadership Insights only. Aggregated buckets, no PII.
- Account deletion
- Employee-initiated. Identity hashed.
- HIPAA
- BAA provisions, lab-report pipeline only.
Four regions. No later move.
India, US, EU and UAE run as separate instances with in-region endpoints and no cross-region sharing. A company picks one during onboarding, and changing it afterwards is a migration rather than a setting.
One tenant, one scope
Every record carries the company it belongs to, including lab and health-risk queries. One customer's data is never in another's result set.
Count only. Never a name list.
An admin opens participation, not people. Health-risk targeting returns how many employees match, and the screen says why.
The list of users is not displayed to protect individual privacy. Shown when a health-risk audience is selected
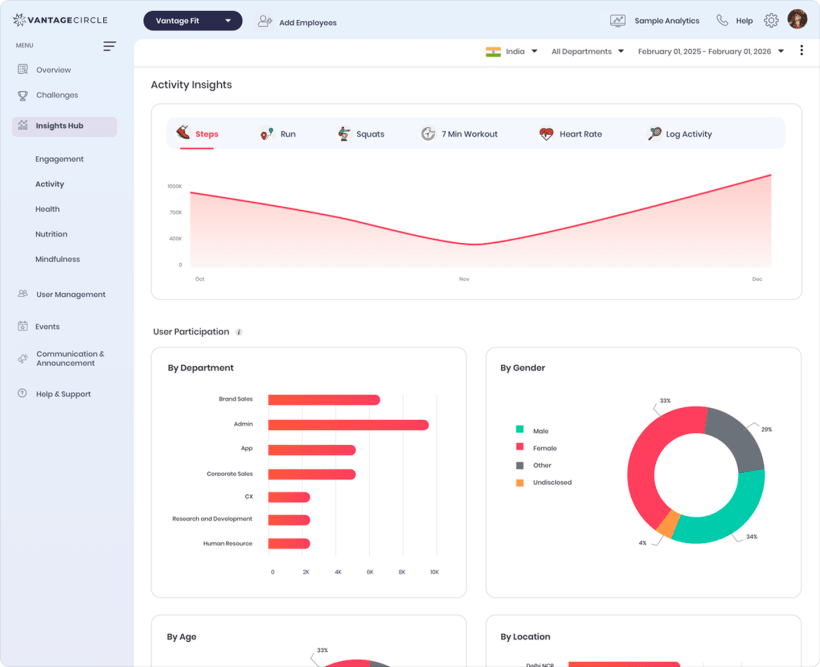
What an admin actually opens. Figures inside the screenshot are sample data.
Access, in numbers.
Single sign-on is SAML 2.0, configured with your identity team rather than switched on from a dashboard. The rest is specific enough to check.
Then the account locks. Unlocking runs through a reset.
Single use, and it expires whether opened or not.
Eight on the reset flow, six on the in-app change. Separate flows.
Configurable per country. Four digits on mobile, six on web.
On the mobile apps.
On non-mobile web and on admin sign-in.
IdP list and provisioning sit on Integrations and SSO.
What leaves, and what stays.
Observations from aggregated buckets through an internal ML API. Read-only, no PII, and it changes no configuration.
Verified by OTP. Name and email are hashed and tokens cleared, while historical activity and transaction records stay for reporting. Company-configurable.
BAA provisions for HIPAA compliance cover the lab-report pipeline. That is HIPAA-guideline aligned, not a HIPAA-compliant platform, and we will not write it as if it were.
Claims this page does not make.
A badge is easy to print. These are the ones we will not print.
Neither is asserted here, and there is no seal anywhere on the page.
EU data residency is available. Residency is a hosting fact and not a compliance verdict.
BAA provisions cover the lab-report pipeline. The platform as a whole is not described as HIPAA compliant.
Neither is live today. Encryption specifics are not published here either, so bring that question to the review.
Before the security review
Can an HR admin see an employee's lab report?
No. Lab and biomarker data is visible to the employee only. HR sees org-level prevalence per health area, and no screen or export exposes an individual's report.
Where does the AI run, and on what?
Leadership Insights only, on aggregated buckets through an internal ML API, with no PII. Lab-report extraction is the other AI surface and sits on the health data upload page. Recommended Actions are rule-based.
Can we choose our data region after go-live?
No. India, US, EU or UAE is set at onboarding and every request after that is served by in-region endpoints. A change is a migration, not a setting.
Send this one to your reviewer.
We will walk residency, tenancy, admin visibility and the sign-in rules with your IT team on the call.
Trusted by 100+ organizations.